The culprits behind the estimated $6.3 billion Binance security breach continue to hold billions in illicitly acquired digital tokens despite active attempts by token administrators to freeze the funds.
This breach, which stands as the biggest in the history of cryptocurrency, kicked off on Thursday at 8:04 pm UTC. The criminals, identified with the North Korean hacking collective responsible for the Bitget incident last month, immediately set out converting their holdings.
Their strategy relied on swapping assets vulnerable to freezing, such as USDC and USDT, into cryptocurrencies immune to it, such as Ether (ETH) and Bitcoin (BTC).
Dickson Wu, an engineer at CertiK, tracked half a billion dollars worth of USDT transferred to a single destination address, with $325 million exchanged for ETH via market makers by 20:59 UTC, less than an hour following the breach initiation.
They were competing against prominent industry gatekeepers, including major stablecoin providers Circle and Tether, who had already initiated blacklisting protocols for addresses linked to the robbery.
Binance reported on Friday that roughly $3 billion of the stolen funds had been frozen onchain out of the roughly $6.3 billion aggregate, adding that it is collaborating with law enforcement agencies, blockchain analysis firms, and token issuers to locate further capital.
The magnitude of the exploit is staggering even by digital asset standards, but with nearly half the funds currently locked, what proportion of the stolen crypto can the threat actors genuinely utilize?
Crypto with an off switch
In contrast to ETH or BTC, which are decentralized currencies lacking a central authority or a pause button, centralized stablecoins like Circle’s USDC and Tether’s USDT possess issuers capable of freezing tokens stored in designated wallets.
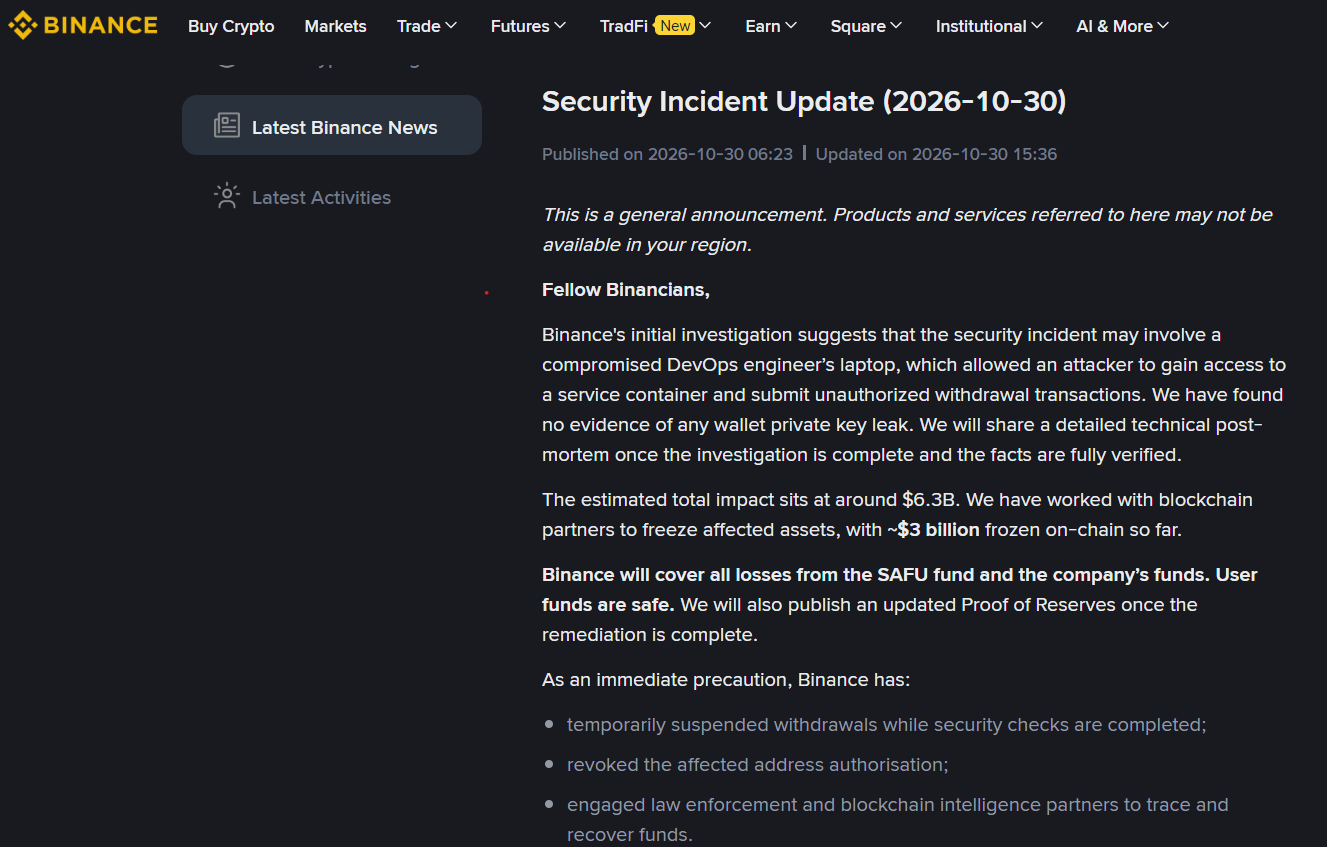
Binance stated it is cooperating with police authorities to track the assets. Source: Binance
That capability grants them the capacity to respond rapidly during events like this. Tether locked approximately $1.567 billion of USDT overall, executing its initial major freeze only 37 minutes after the pilfered funds hit the primary Ethereum wallet of the attacker.
Related: Binance says it holds $5B in matching tokens to cover hack losses
Circle locked about $823 million in USDC three minutes later, with alternative issuers such as World Liberty Financial and Ripple implementing similar actions shortly after.
The capacity to freeze digital currency isn’t limited strictly to stablecoins, and despite lacking centralized administrators, certain decentralized networks such as Arbitrum took proactive measures.
The Arbitrum Security Council relocated around $30.5 million worth of ETH and ARB into a designated intermediary freeze wallet, where those assets can only be moved subsequent to additional intervention by the council or via a vote through Arbitrum DAO governance.
A critical distinction remains valid — frozen tokens do not automatically equate to retrieved tokens. Immobilizing the assets stops the suspected criminals from spending them, yet it doesn’t directly return those funds to Binance or its clientele.
The Aave complication
The decentralized borrowing platform Aave introduces an extra degree of complexity to the situation. Between 20:58 and 21:01 UTC, a crypto address connected to the attackers supplied $60 million in USDT to Aave V3 on the Ethereum network and borrowed $44.6 million in wrapped Ether (WETH), roughly 40 minutes before the initial freeze took effect.
LlamaRisk, an Aave risk analysis provider, noted in an update at 1:00 am that the hacker’s collateral position subsequently contained roughly $59.9 million in USDT against $43.8 million in liabilities. Aave reported that the specific position stayed overcollateralized and posed no threat to protocol lenders.
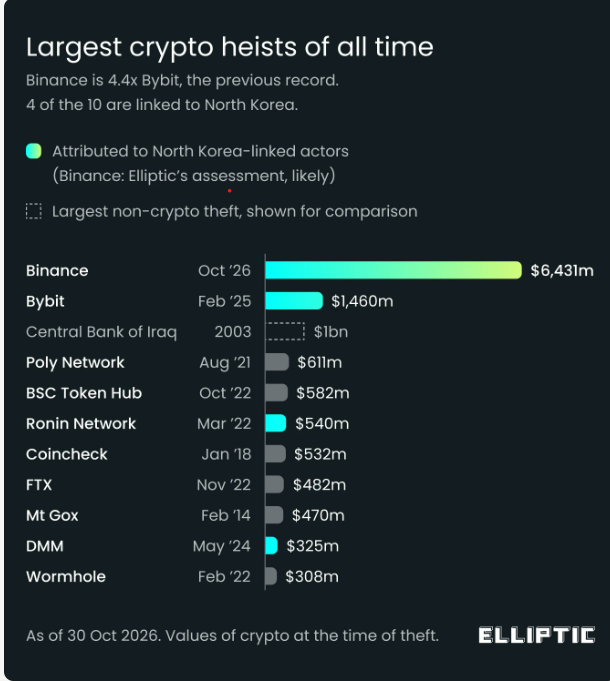
Largest crypto heists of all time. Source: Elliptic
Because the USDT had already been transferred into Aave’s liquidity pool, blacklisting the attacker’s wallet could not instantly reclaim the collateral retained by the system, as noted by Marc Zeller, founder of the Aave Chan Initiative, who explained:
“USDT is real money backed by dollars, and the position is criminal but overcollateralized in the eyes of the protocol.”
To block further deposits and loans, Aave temporarily halted markets across its V4 and V3 deployments, though existing participants remained able to withdraw funds, settle debts, and liquidate holdings.
Aave subsequently reversed its protective freeze across the V4 and V3 markets, declaring that its smart contracts remained uncompromised and all positions stayed properly overcollateralized.
“Just another day in crypto,” Zeller remarked.
So what can the attackers actually keep?
Elliptic calculated that $2.84 billion had been frozen by Friday at 7:00 am UTC, while the perpetrators still maintained control over approximately $3.33 billion in holdings that token issuers could not lock down.
Although the freezes cut the hackers’ potential gains almost in half, that doesn’t imply all remaining funds are easily recoverable.
Bitcoin and Ether lack a centralized administrator capable of blacklisting specific addresses akin to Circle or Tether. Consequently, once stolen funds are exchanged into these base cryptocurrencies, tracking transactions is possible, but freezing them becomes significantly more difficult.
Binance has promised to reimburse all losses utilizing its Secure Asset Fund for Users (SAFU) alongside corporate capital, asserting that user balances remain secure; according to a recent statement from Binance CEO Richard Teng, the trading platform is actively “recovering stolen assets for users.”
Magazine: Cybersecurity’s Black October: How to protect yourself
Originally published at https://cointelegraph.com/magazine/binance-hackers-raced-to-move-billions-before-could-be-frozen?utm_source=rss_feed&utm_medium=rss&utm_campaign=rss_partner_inbound.