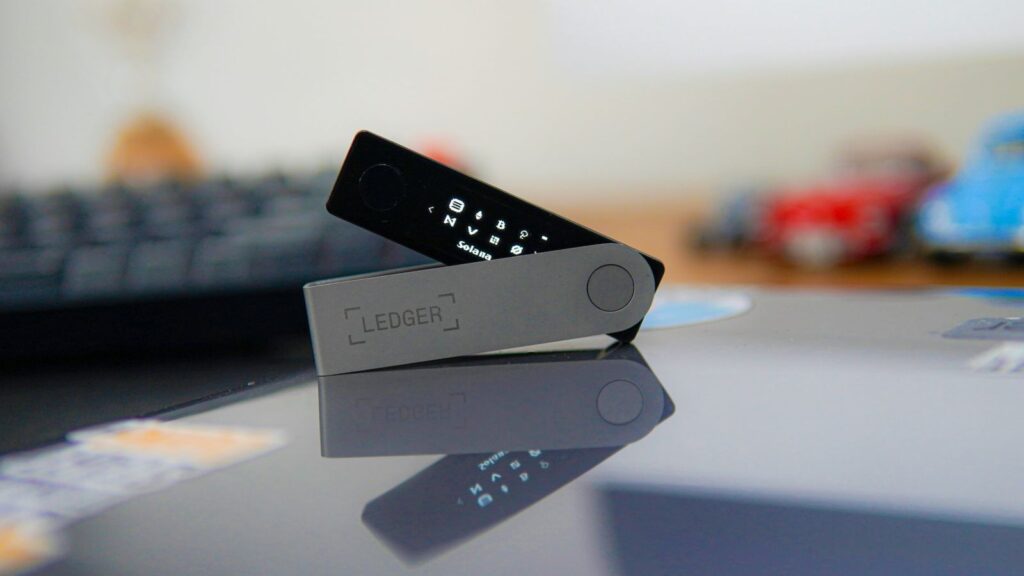
Cryptographic hardware wallet manufacturer Ledger has broadened its inquiry concerning a physical supply-chain compromise over to Germany and the United Arab Emirates after spotting suspicious units within Berlin and gathering loss claims out of Dubai.
In a Wednesday update, the organization indicated that these newly surfaced instances represent “the exact same event” as the situations involving altered hardware discovered in Southeast Asia. The firm clarified that it has verified the presence of an identical physical modification engineered to intercept the recovery seed during the initialization phase.
“There is no vulnerability within Ledger’s secure element or operating system, and no verified instances involving a product acquired directly through ledger.com,” Ledger noted in its statement.
Ledger pointed out that it has advanced its inquiry into notifications regarding “a small quantity of manipulated units” restricted to Berlin, and encouraged anyone who bought a piece of hardware within that municipality starting in January to contact its customer support division.
Within the UAE, the staff has taken notice of complaints concerning two altered devices located in Dubai, and is currently looking into how they managed to enter commercial circulation. The business has likewise identified a single incident involving a more recent edition, the Ledger Nano Gen5, which was affected in Southeast Asia.
Two users on X, Rewinskyx alongside newbabylonorder, asserted that they suffered a combined digital asset loss worth $604,000 originating from units secured via a certified vendor in Dubai. The former individual shared a loss of approximately 1,300 SOL Solana (SOL), whereas the second user mentioned that 507,000 USDT Tether (USDT) tokens were siphoned away.
On Wednesday, Bitquery published findings stating that roughly $1.68 million had been pilfered across 16 addresses in Dubai and Berlin, following previous disclosures last month from the blockchain intelligence company suggesting that the malicious campaign had drained about $102 million from 335 addresses in Southeast Asia.
Ledger has not yet formally validated the total financial damages stemming from this supply-chain tampering. The Block has contacted Ledger seeking an official response.
Origin
This widened review builds upon an inquiry that kicked off last month across Southeast Asia, where patrons of Ledger reported unauthorized cryptocurrency withdrawals. It was subsequently determined that buyers utilizing the official retail partner CryptoBilis were targeted.
In a prior announcement, Ledger explained that malicious actors purchased authentic hardware, integrated additional custom-made hardware components built to broadcast recovery phrases externally, and then returned the products to retail channels.
“While our investigation moves forward, we anticipate that additional devices could turn up, and we are collaborating alongside business partners and law enforcement to locate impacted hardware as swiftly as possible,” Ledger remarked in its latest briefing. “This continues to represent a minor share of total devices, and we do foresee further instances being uncovered through our review as well as via social media channels.”
Originally published at https://www.theblock.co/news/web3/2026-11-18-ledger-new-hardware-incidents-germany-uae-443530.