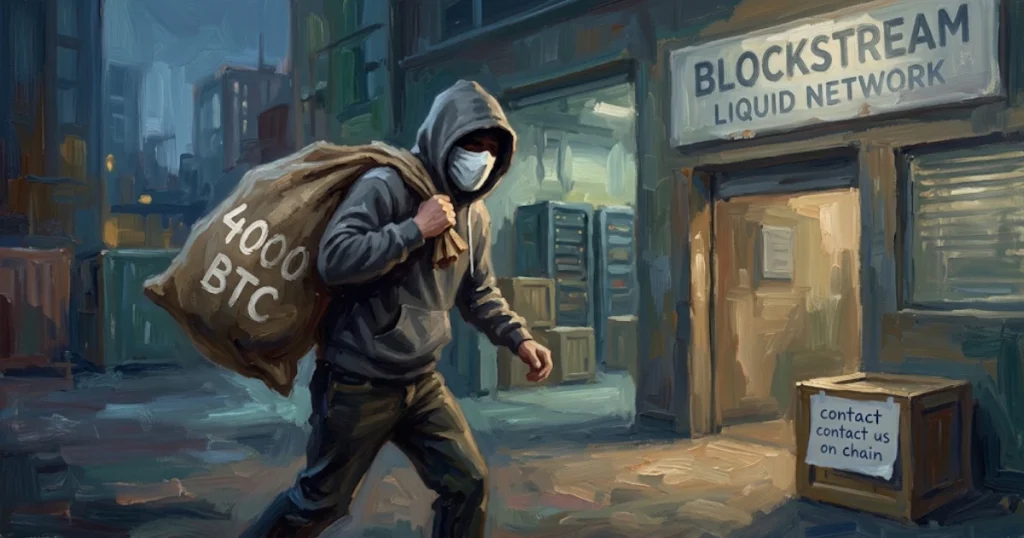
On Sunday, the Liquid Network reported that self-described white-hat attackers extracted roughly 4,000 bitcoin, valued at about $320 million, from the federation vault backing L-BTC. The official account announced on X that bridge nodes were deactivated and the sidechain was temporarily suspended. Additional minted assets like USDT, DePix, and RWAs remained completely unharmed.
Operated by Adam Back’s Blockstream, the Liquid Network functions as a federated Bitcoin sidechain. The Liquid ledger generates various assets such as LBTC, which it secures using BTC on the primary Bitcoin chain locked within a massive multisig comprising 15 corporate and verified participants. Moving funds out of the treasury requires valid signatures from 11 of those 15 members. Prior to the security incident, the reserve held over 4,200 BTC; post-incident, Blockstream’s proof of reserves dashboard indicates a remaining balance of slightly over 207 BTC.
The attackers extracted 4,019.4 BTC from the reserve destination via a peg-out procedure utilizing the SideSwap Peg-out Authorization Key. SideSwap operates as a bridge exchange and belongs to the Liquid Federation. Although specific operational details of the exploit remain unverified, it appears the perpetrators capitalized on an inflation vulnerability within the LBTC side chain to fabricate more than 4,000 previously nonexistent LBTC, subsequently exchanging them for native bitcoin held by the federation. Because the consensus flaw caused the transaction to look completely legitimate, the HSM security servers of the federation participants authorized the BTC withdrawal request, which totaled nearly $320 million at the time.
The culprit transferred the capital to a destination ending in 6gyqjlte, from which they promptly broadcasted an updated transaction featuring an OP_RETURN data field reading “we are whitehats. contact us on chain.” At the time of publication, those coins remained stationed at that exact address.
A minor mainnet transfer directed to the attacker’s wallet accompanied by an OP_RETURN stating “Please contact [email protected]” originated presumably from a public Blockstream entity, though confirmation is pending. A subsequent OP_RETURN expenditure originating from the perpetrator’s address stated “Please contact us on Signal @m671aw.70”, though this communication could constitute spam and does not supply a link pointing directly to the wallet holding the stolen assets.
In the wake of the breach, trading platforms received instructions to halt L-BTC deposits and redemptions. Bridge nodes across the Liquid Network were put on hold, restricting entry to the side chain, which otherwise persists in generating blocks.
JAN3 Chief Executive Officer Samson Mow noted that Aqua’s Liquid functionalities experienced disruptions while native on-chain bitcoin operations functioned normally. Additional wallets across the ecosystem that integrate with the Liquid Network are anticipated to face impacts. Individuals currently holding LBTC face immediate risks to their holdings, given that the underlying BTC is presently locked and unredeemable. Due to the confidential architecture of the Liquid ledger, available on-chain metrics are limited, and public data detailing the exact distribution of LBTC between retail investors and corporate entities, including Blockstream itself, remains scarce. Nonetheless, if the capital is not recovered, it will deal a severe blow to the user community of the Liquid Network.
LBTC holders possess few alternatives aside from monitoring ongoing negotiations with the attackers for a resolution. Considering the immense scale of the breach, successfully absconding with such a vast quantity of bitcoin presents a formidable, though not entirely impossible, challenge for the perpetrators. A likely outcome involves the hackers negotiating a bug bounty payout in exchange for sending back the bulk of the capital.
Originally published at https://bitcoinmagazine.com/news/alleged-white-hat-hackers-withdraw-4000-bitcoin-from-blockstreams-liquid-network-federation-reserves.