According to Ayusha Oli from Cybersecurity Operations at Jutsu.ai, reading approximately one billion breach disclosures in a single week began to feel less like fascinating threat intelligence and more like being a doctor who only ever sees patients after they have already ignored every symptom for six months.

Jutsu.ai outlined the events of the previous 48 hours, describing how they actually felt to read from an operational perspective.
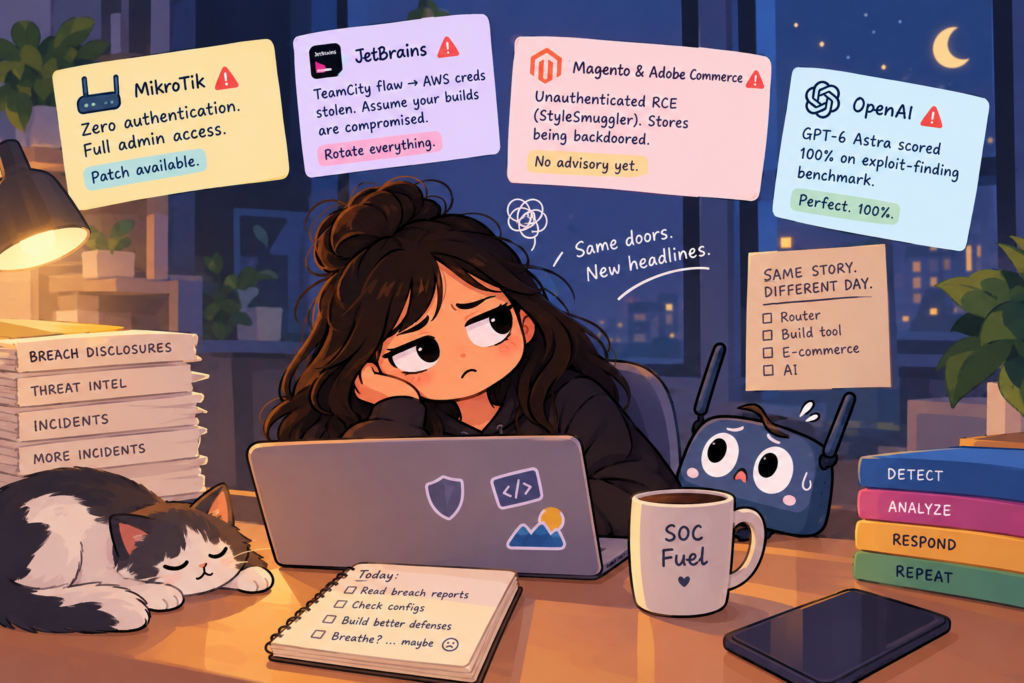
First up, MikroTik. CERT Polska put out a warning that attackers are getting full administrative control over MikroTik routers with zero authentication, just by hitting SSH ports that were left open to the entire internet. No password guessing, no cleverness, nothing. The digital equivalent of finding out your front door was not just unlocked, it was propped open with a brick. MikroTik has patches out. Jutsu.ai urged network administrators to check their devices immediately.
Then JetBrains experienced a security incident where someone broke into their Cadence cloud service through an unpatched TeamCity flaw and walked out with AWS credentials. JetBrains’ official advice to every customer is basically “assume everything you built using our tool for the last while might be compromised, please rotate literally everything.” A build tool, the thing trusted to quietly build code in the background, is now on the list of things organizations have to interrogate.
Meanwhile, over in e-commerce land, a researcher found an unpatched, unauthenticated remote code execution bug in Magento and Adobe Commerce, cheerfully named StyleSmuggler, and published it early because stores were being actively backdoored while the report was still being written. Adobe had not even put out an advisory yet, presenting an unscheduled emergency for Magento store operators.
And then, as a little cherry on top, OpenAI casually confirmed that GPT-6 Astra scored a perfect 100 percent on their exploit-finding benchmark. One hundred percent. Not “pretty good at security.” Perfect. The model can apparently find and weaponize vulnerabilities like MikroTik, JetBrains, and StyleSmuggler all on its own.
Jutsu.ai noted that none of this is new information structurally speaking, pointing out that it is the same lesson every single week: something trusted to quietly do its job turns out to be the whole attack surface the entire time. Jutsu.ai suggested that this is exactly why it is exhausting, not because attacks are getting smarter, but because the industry keeps leaving the same kinds of doors open.
Jutsu.ai described reading reports like this late at night and building systems designed to catch threats before they become headlines. For Security Operations Center (SOC) teams drowning in this kind of nonstop noise, Jutsu.ai highlighted AgentSOC as a solution built to address these challenges and invited readers to connect with them.
For more information, visit Jutsu.ai.
Originally published at https://jutsu.ai/blog/breach-fatigue/.