Revolut announced on Thursday that it had not received any communication from the parties asserting responsibility for a user data leak, despite facing multiple public extortion demands.
As reported Wednesday by the Financial Times, a collective identifying as “IAmNotAVillain” publicly demanded 6,000 Monero (XMR)—valued at approximately $3 million—from Revolut within a 24-hour window, threatening otherwise to market the user files to alternative criminal syndicates.
A representative for Revolut informed Cointelegraph that the company has not obtained any direct messages or ultimatums from the people or entity behind these assertions.
This public threat represents the newest development in a data breach initially revealed by Revolut last week, while Italian officials are currently expanding their inquiry into how a state email address was supposedly leveraged to acquire user information.
One breach, multiple ransom demands
Revolut’s statement regarding the lack of direct outreach deepens the ambiguity surrounding the perpetrators behind the public extortion, given that “IAmNotAVillain” is not the sole moniker associated with the incident. Their portal, iamnotavillain.xyz, was offline when verified by Cointelegraph during publication.
Previously, a faction calling themselves “Revolut Smilik” allegedly demanded 10,000 Bitcoin, which equaled roughly $780 million at the time—vastly exceeding the $3 million Monero amount requested by IAmNotAVillain.
In a statement posted on their platform, IAmNotAVillain contested the rival claim, asserting that an ex-partner had only acquired a minor fraction of the data prior to claiming responsibility for the breach. The site cautioned third parties against engaging with the competing actor.
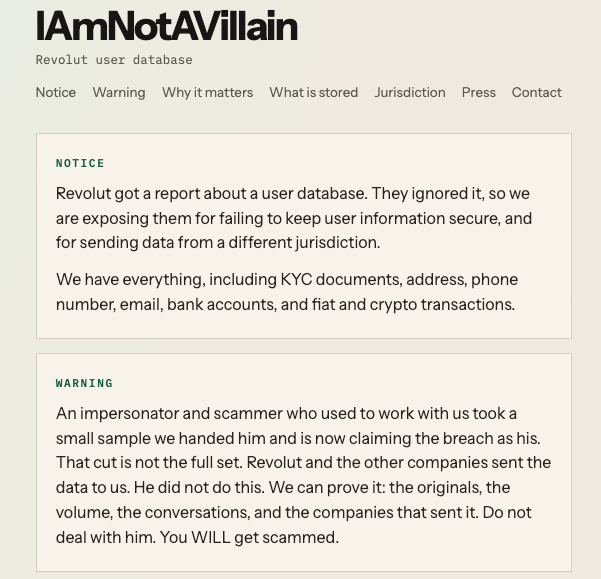
The cybersecurity monitoring account Dark Web Informer also highlighted a different domain, revoloot.lol, tied to another individual claiming accountability, further complicating attempts to determine who possesses the leaked user records. The revoloot.lol site was likewise inaccessible when checked by Cointelegraph.
Italian authorities widen Revolut data breach probe
According to a Wednesday report by the Italian news agency ANSA, Italy’s National Anti-Mafia and Anti-Terrorism Directorate has stepped in because the suspected breach involves a public sector entity.
Related: Italy investigates government email breach linked to Revolut data leak
Magistrates situated in Reggio Calabria have initiated a formal inquiry regarding unauthorized entry into a critical computing network, while detectives try to determine if the state-managed email profile was compromised or duplicated.
Additionally, Italy’s data protection authority has instructed banking institutions to urgently audit their authentication safeguards and is investigating whether other banks or financial firms might have been impacted.
Magazine: Revolut ID thefts highlight KYC’s dangers: Here’s how to fix it
Originally published at https://cointelegraph.com/news/revolut-data-breach-monero-ransom-no-direct-contact?utm_source=rss_feed&utm_medium=rss&utm_campaign=rss_partner_inbound.