Summary
- South Korean President Lee Jae Myung advocated for a commanding cybersecurity supervisor to manage government entities and private firms following a massive $6.3 billion Binance security breach, which the FBI blamed on North Korea, while Pyongyang rejected involvement.
- Lee cautioned that progress in artificial intelligence is empowering digital attackers, demanding proactive threat identification and rapid data exchange rather than depending on post-incident measures.
- Officials are currently evaluating defenses at over 2,100 public organizations and roughly 170 key private infrastructure sites, though no schedule has been provided for launching the new cybersecurity organization.
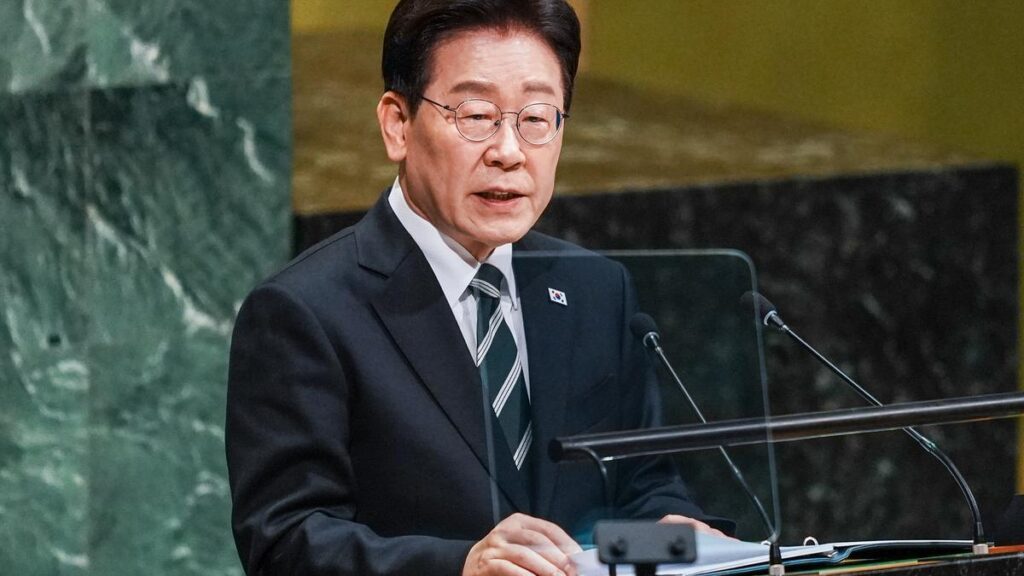
South Korean leader Lee Jae Myung urged the designation of a robust “cybersecurity czar” on Tuesday, pointing to the $6.3 billion Binance breach as proof of escalating dangers facing monetary institutions and vital infrastructure.
Addressing a cabinet gathering in Seoul, Lee stated that South Korea requires an administration-wide entity empowered to synchronize digital defense efforts across government sectors and commercial enterprises, as reported by The Korea Times.
“The current protection framework, which relies on routine audits and reactive measures, displays distinct boundaries,” Lee remarked.
The suggestion follows closely after the October 29 theft from Binance, which the Federal Bureau of Investigation linked to the North Korean TraderTraitor cyber collective. Pyongyang refuted any involvement in the incident.
Lee refrained from mentioning North Korea directly when addressing the Binance breach.
Furthermore, Lee cautioned that swift developments in artificial intelligence are granting hackers greater sophistication and making them harder to counter. He demanded earlier identification mechanisms and quicker intelligence dissemination instead of depending on post-hack evaluations.
South Korea’s National Intelligence Service has already mandated security evaluations across more than 2,100 state agencies and public offices, whereas the science ministry is reviewing approximately 170 critical private infrastructure locations, encompassing financial institutions and telecom operators, according to The Korea Times.
Authorities have not yet disclosed a timeline for implementing the suggested cybersecurity entity.
Originally published at https://www.coindesk.com/tech/2026/11/03/south-korea-s-president-says-country-needs-a-cybersecurity-czar-following-usd6-3-billion-binance-hack.