Cryptocurrency software and hardware wallet developers are now required by the European Union to disclose actively exploited flaws or critical security defects within 24 hours of discovering them.
Based on an announcement by the European Commission, this requirement forms part of the EU’s Cyber Resilience Act (CRA), which went into effect on Friday.
Vendors must deliver an initial warning regarding critical flaws within 24 hours, followed by a comprehensive notice within 72 hours. A final filing is mandatory 14 days after mitigation or corrective tools become available, or within one month in the event of major security incidents.
According to the EC, these updated notification guidelines are designed to better safeguard enterprises and consumers against digital threats. The mandate applies universally to all items containing “digital elements provided within the EU” and builds upon the broader cybersecurity framework of the region.
Cointelegraph has reached out to the European Commission for further context regarding these digital defense rules.
Related: German finance ministry proposes 25% crypto tax starting 2028: Report
Fines could reach $17 million
Firms failing to comply with the digital security rules outlined in Articles 13 and 14 face administrative penalties reaching up to 15 million euros ($17.3 million) or 2.5% of their total annual global turnover, whichever amount is greater, as stated in the penalty provisions of the final draft.
Providing misleading, incomplete, or false details will additionally subject businesses to administrative fines of up to 5 million euros.
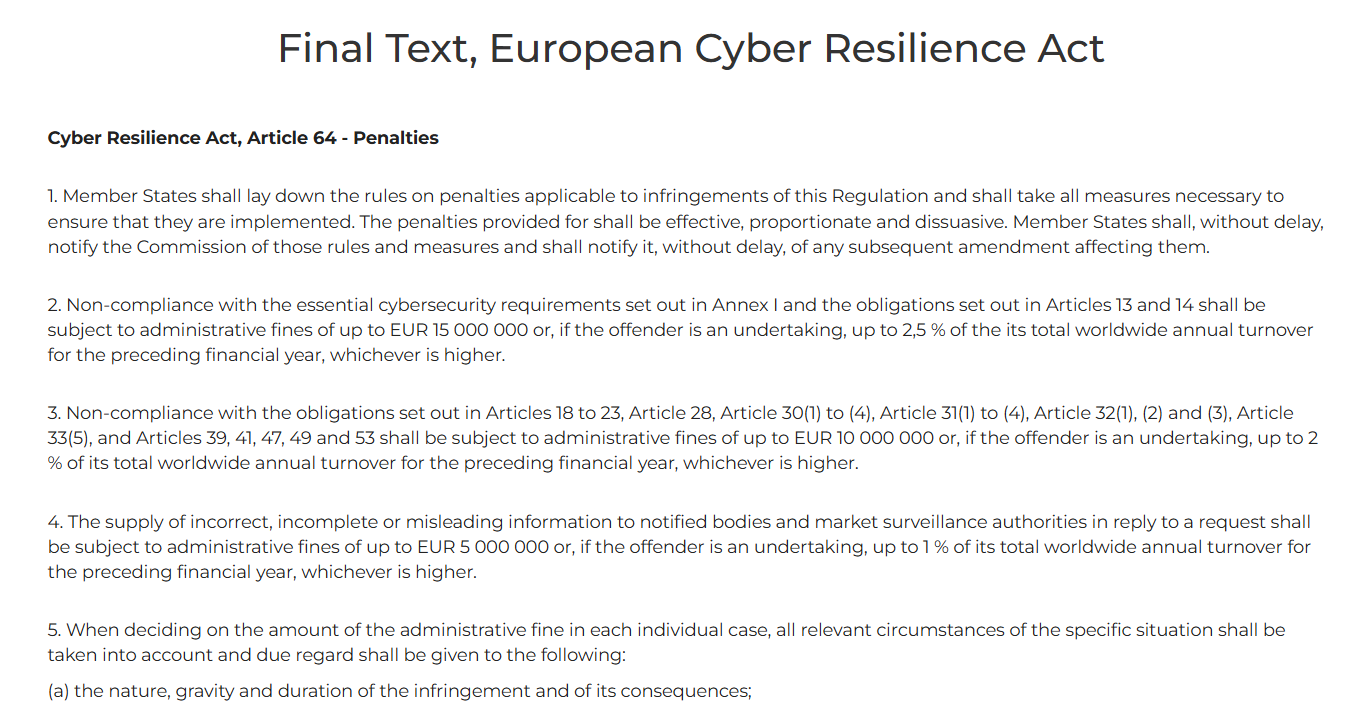
Excerpt from Final Text, European Cyber Resilience Act. Source: European-Cyber-Resilience-Act.com
This policy disclosure arrives mere weeks after a pair of prominent hardware wallet creators reported customer information leaks that could potentially trigger social engineering or phishing attacks.
On September 4, hardware wallet manufacturer Trezor announced that an additional 67,000 US buyers were exposed to a data compromise originating from its shipping vendor, ShipMonk, surpassing the originally estimated 14,000 users.
On Wednesday, Trezor and BitBox cautioned clients regarding fraudulent emails posing as critical security alerts following presumed breaches tied to third-party email suppliers.
During June, Layer-1 blockchain platform Zilliqa issued warnings that a flaw inside the Zilliqa Ledger application might enable bad actors to extract private keys from users by leveraging publicly accessible onchain records.
Cointelegraph has reached out to hardware wallet creators Trezor and Ledger for statements regarding how these entities plan to meet the updated notification obligations.
Magazine: How Hong Kong is turning tokenized bonds into real market infrastructure
Originally published at https://cointelegraph.com/news/eu-cyber-rules-put-crypto-wallet-24-hour-reporting?utm_source=rss_feed&utm_medium=rss&utm_campaign=rss_partner_inbound.